From matching known files to watching behaviour
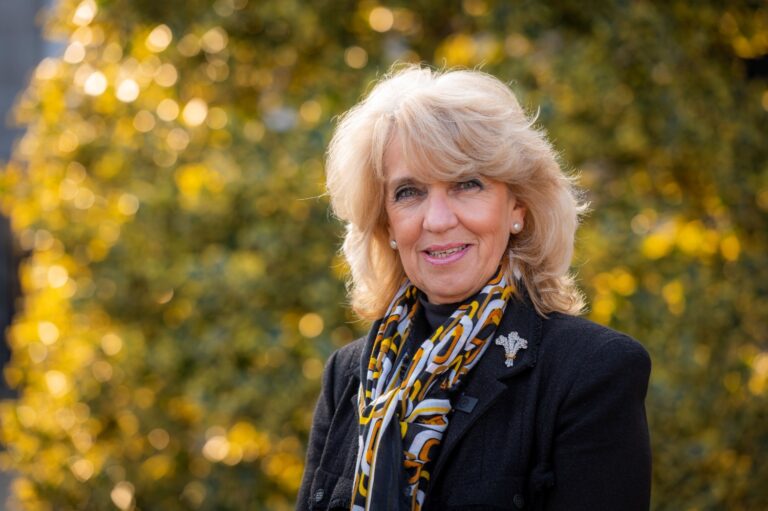
Antivirus has moved well beyond spotting known bad files. “Modern endpoint protection watches behaviour, context and patterns instead,” says Angela Pringle, Cyber Security Lead at CyberLogic. That shift, from traditional antivirus to endpoint protection platforms (EPP), endpoint detection and response (EDR) and extended detection and response (XDR), reflects a change in what defenders are actually looking for today. Not simply blocking malware, but spotting what an attacker does once they are already inside an environment: persistence, privilege escalation, credential theft and lateral movement.
This matters because a growing share of intrusions no longer rely on malware at all. According to CrowdStrike’s 2026 Global Threat Report, 82% of 2025 detections were malware-free, a sign of how often attackers now operate through legitimate credentials, tools and trusted systems rather than files an antivirus product would recognise as malicious. “Antivirus is evolving into something less about a product on a laptop and more about visibility and response across the whole environment,” says Pringle.
AI hasn’t created a new kind of attack, it’s created faster attackers
Pringle is cautious about framing AI-generated attacks as simply “better malware.” The more significant change, she says, is speed and accessibility: AI accelerates reconnaissance, social engineering and scripting, and lets attackers with limited skill carry out intrusions that previously required real expertise. CrowdStrike’s 2026 report recorded an 89% year-on-year rise in AI-enabled attacks, with the fastest observed breakout taking just 27 seconds.
Because attackers increasingly “live off the land”, abusing legitimate tools and stolen credentials rather than deploying custom malware, traditional antivirus often has nothing obvious to flag. “Keeping pace means strong behavioural detection and automated response,” says Pringle. “It’s about building a security operation that moves at AI speed, not finding a product that solves AI.”
Treat every AI agent like a privileged user
The same speed that makes AI valuable to attackers makes it risky when organisations deploy their own agents carelessly. Pringle’s test for whether a process is ready to hand to an AI agent is simple: it needs to be well-defined, repeatable and measurable. “Hand an AI agent a messy process and you just get a bad process happening faster,” she says.
The stakes are not hypothetical. A 2026 State of AI Agent Security survey found that 54% of organisations had experienced or suspected an AI-agent security or data-privacy incident in the previous 12 months. Pringle’s recommendation is to onboard an agent the way a security team would onboard a privileged user: start with least privilege, log everything, keep human approval on high-impact actions, and test in a controlled environment before expanding permissions – then actively check whether those permissions can be abused, bypassed or escalated.
Antivirus is a control, not the strategy
For Pringle, there is no longer a clean line between antivirus and cybersecurity more broadly. Endpoint protection is one control among many, and it can’t address compromised credentials, cloud misconfigurations or social engineering on its own. Verizon’s 2026 Data Breach Investigations Report found that vulnerability exploitation has overtaken stolen credentials as the leading way attackers gain initial access, accounting for 31% of breaches.
“The best way to know whether your controls hold up is to test them from an attacker’s perspective,” says Pringle. A penetration test or red-team exercise reveals whether someone who gets past the endpoint can still escalate privileges, move laterally or reach sensitive data. Antivirus, in her view, needs to sit alongside identity, cloud security, application security and incident response – “a piece of the strategy, not the strategy.”
Who owns endpoint security when it fails?
Responsibility for endpoint security, Pringle argues, is shared rather than owned by one team. IT manages the devices and deployment, security defines requirements and responds to alerts, employees interact with the endpoint every day, and leadership funds and prioritises the investment. “A great platform that’s under-resourced won’t deliver,” she says.
Security teams, she adds, should validate their own assumptions through penetration testing and red teaming rather than assuming a deployed control is a working one. “Knowing a control is deployed and knowing it works under attack are two different things,” says Pringle. “The real question isn’t who owns the antivirus, but who’s accountable when protection fails.”